


Question
securing the cfglobal cookie
Our company was doing security scans on our https website and reported to me that the cfglobal cookie is not being served securely. I did some reading and tried the following solutions to fix this. After checking the headers I still have an unsecured cfglobal cookie. Here's what I tried:
- CF Administrator -> Memory Varialbles -> Check Secure Cookie and HTTPOnly
- in Application.cfc added the following cfscript code:
- this.sessioncookie.httponly = true;
- this.sessioncookie.secure = "true"
Header:
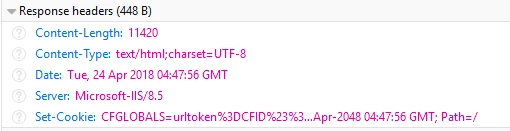
I don't know what else to do. I thought checking secure cookie in CF Administrator forces all the cookies to be served securly???
 AdChoices