


jeffreywh
Participating Frequently
Apr 17, 2015 4:17 PM UTC
Question

Has anyone else run into security issues with whstub.js, whproxy.js, whtopic.js, ehlpdhtm.js, and whfhost.js?

We have a customer's security team objecting to the files because of an issue with their "Overly Permissive Message Posting Policy." An example:
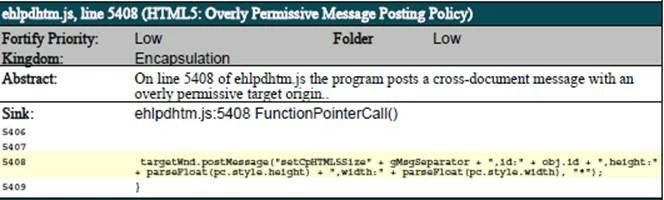

Has anyone else run into this, and is there anything we can do to reduce the threat assessment?

This topic is closed to new replies. Start a new post to keep the conversation going.

3 replies

Captiv8r
Legend
Apr 18, 2015 2:56 PM UTC

Perhaps try using Responsive HTML as an output type?

Translate
Willam van Weelden
Inspiring
Apr 20, 2015 1:13 PM UTC

Even then there's still a lot of messages going forward and the ehlpdhtm.js is shared across outputs.

But the postMessage option used is safe since you need to write code specifically for getting these messages. No hijacking can just be done through this. (See also Window.postMessage() - Web API Interfaces | MDN)

The concern here is the domain policy in the call where the * is too permissive. But since the help can be placed on any given URL, there is no way for Adobe to do it differently. Personally, I don't believe this is an issue as postMessage is meant for secure communication and it's not something you can just hijack.

Translate
jeffreywh
jeffreywhAuthor
Participating Frequently
Apr 20, 2015 7:04 PM UTC

I will pass that along. I'm not in direct contact with the customer's security people, so I don't know their level of concern beyond what was passed to me.

In any case, thanks!

Translate